In particular, the NO-SHA1 module still permits using SHA-1 with hash-based message authentication codes (HMAC). This is as a result of HMAC security properties do not rely on the collision resistance of the corresponding hash function, and therefore the latest attacks on SHA-1 have a considerably lower influence on using SHA-1 for HMAC. Let’s configure an OpenSSH server to only provide the AES 256-bit variant of symmetric ciphers for an ssh connection. To apply the change restart the sshd service and verify the ciphers then check you probably can nonetheless login by opening a new session.
As such, the set of enabled algorithms or acceptable key sizes in any offered policy might change during the lifetime of Pink Hat Enterprise Linux. For the opposite phases within the ssh connection, like key exchange, or public key authentication, different expressions for the grep command have for use. This will listing supported key trade algorithms, ciphers, MACs, and extra. Nmap is a strong community scanning software that may also be used to enumerate the SSH algorithms supported by a server using the ssh2-enum-algos script. This demonstrates that while weak algorithms are available as fallback choices, the SSH implementation appropriately prioritizes safe modern algorithms when both shopper and server assist them.
Understanding Ssh Cryptographic Components: Hmacs, Ciphers, Kex, And Macs
If your vulnerability stories have flagged these, you need to explicitly remove them out of your crypto-policy setup. From our findings, after applying the SSH hardening insurance policies, a re-analysis of the SSH algorithm negotiation above reveals that only sturdy algorithms are actually being provided. Particularly, we not see weak algorithms corresponding to hmac-sha1 or diffie-hellman-group14-sha1 in the listing. As An Alternative, only secure algorithms like curve25519-sha256, email protected, and hmac-sha2-256 are negotiated. As you can see, the weak algorithms that were present before hardening have been efficiently eliminated.
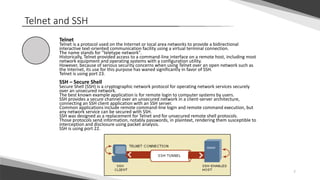
An HMAC (Hash-based MAC) is a common sort of MAC that makes use of a cryptographic hash perform (like SHA-1 or SHA-2) mixed with a shared secret key. Legacy methods or software program does not should support the more trendy and stricter algorithms and protocols enforced by the FUTURE policy. For instance, older techniques won’t assist TLS 1.3 or bigger key sizes. The fips-mode-setup software, which switches the RHEL system into FIPS mode, uses this coverage internally.
- You can use the concept of scoped policies and the option of using wildcards in RHEL eight.5 and newer.
- Let’s configure an OpenSSH server to only provide the AES 256-bit variant of symmetric ciphers for an ssh connection.
- In explicit, the NO-SHA1 module nonetheless allows the use of SHA-1 with hash-based message authentication codes (HMAC).
- With Out correct validation, vulnerable settings may silently persist, especially if coverage modules or defaults were not utilized as intended.
Safety Vulnerability: Deprecated Ssh Cryptographic Settings
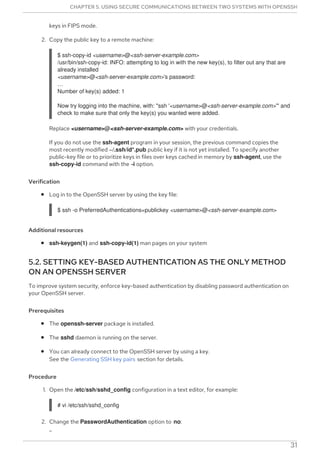
Key Exchange (KEX) is step one in setting up an SSH connection. It allows the client and server to securely agree on a shared secret key with out ever sending the necessary thing over the community. The /etc/crypto-policies/state/CURRENT.pol file lists all settings within the presently utilized system-wide cryptographic policy after wildcard enlargement.
5 Excluding An Application From Following System-wide Cryptographic Policiescopy Linklink Copied To Clipboard!
The following text lists, in detail, the algorithms which are either completely eliminated or disabled in the completely different crypto policy levels in RHEL-8. For a excessive level description of the change see this weblog submit and this kbase article. Changes may be made in the /etc/ssh/sshd_config file to disable the deprecated ciphers and key trade algorithms. Also, create the next crypto policy module to disable the Diffie-Hellman Group14 key trade algorithms (diffie-hellman-group14 and diffie-hellman-group14-sha1) on RHEL 8. For example, if you should disable weak SSH algorithms similar to legacy ciphers and outdated MACs, you’ll find a way to create a customized module and apply it as a part of a CUSTOM cryptographic policy. While DEFAULT is acceptable for so much of environments, it nonetheless allows weak algorithms, including hmac-sha1, hmac-sha1-etm, and even some CBC-mode ciphers (especially in RHEL 8).
Once the server boots, validate all your functions are working as anticipated. A Number Of related choices come into play later throughout consumer authentication. We deliver hardened options that make it easier for enterprises to work throughout platforms and environments, from the core datacenter to the network edge. Also, using sturdy algorithms usually will increase the computational workload, which could negatively have an result on your system efficiency. Vulnerability classification has been carried out utilizing the CVSS v3.1 scoring system .
Earlier Than diving into remediation, it’s essential to verify whether the vulnerabilities, such as these flagged within the Rapid7 report, actually exist in your surroundings. In our case, while we didn’t discover 3DES or MD5 algorithms in use, we did verify that HMAC-SHA1 was still lively, which was flagged as a weak algorithm. Which will list all of the configuration choices, including the chosen values forthe Ciphers, MACs, HostKeyAlgorithms andKexAlgorithms parameters. You can use the concept of scoped insurance policies and the choice of utilizing wildcards in RHEL 8.5 and newer.
Updating Configuration And Removing Ciphers
The system-wide cryptographic policies is a system element that configures the core cryptographic subsystems, overlaying the TLS, IPsec, SSH, DNSSec, and Kerberos protocols. It supplies a small set of policies, which the administrator can select. These ciphersuites and protocols are fully faraway from the core crypto libraries. They are either not present at all in the sources or their assist is disabled through the build so it can’t be used by functions in any way. This ensures the SSH daemon picks up the updated cryptographic settings from the new policy. While CBC ciphers are removed, the presence of hmac-sha1 and email protected remains https://falcoware.com/FalcoManager.php a security concern.